
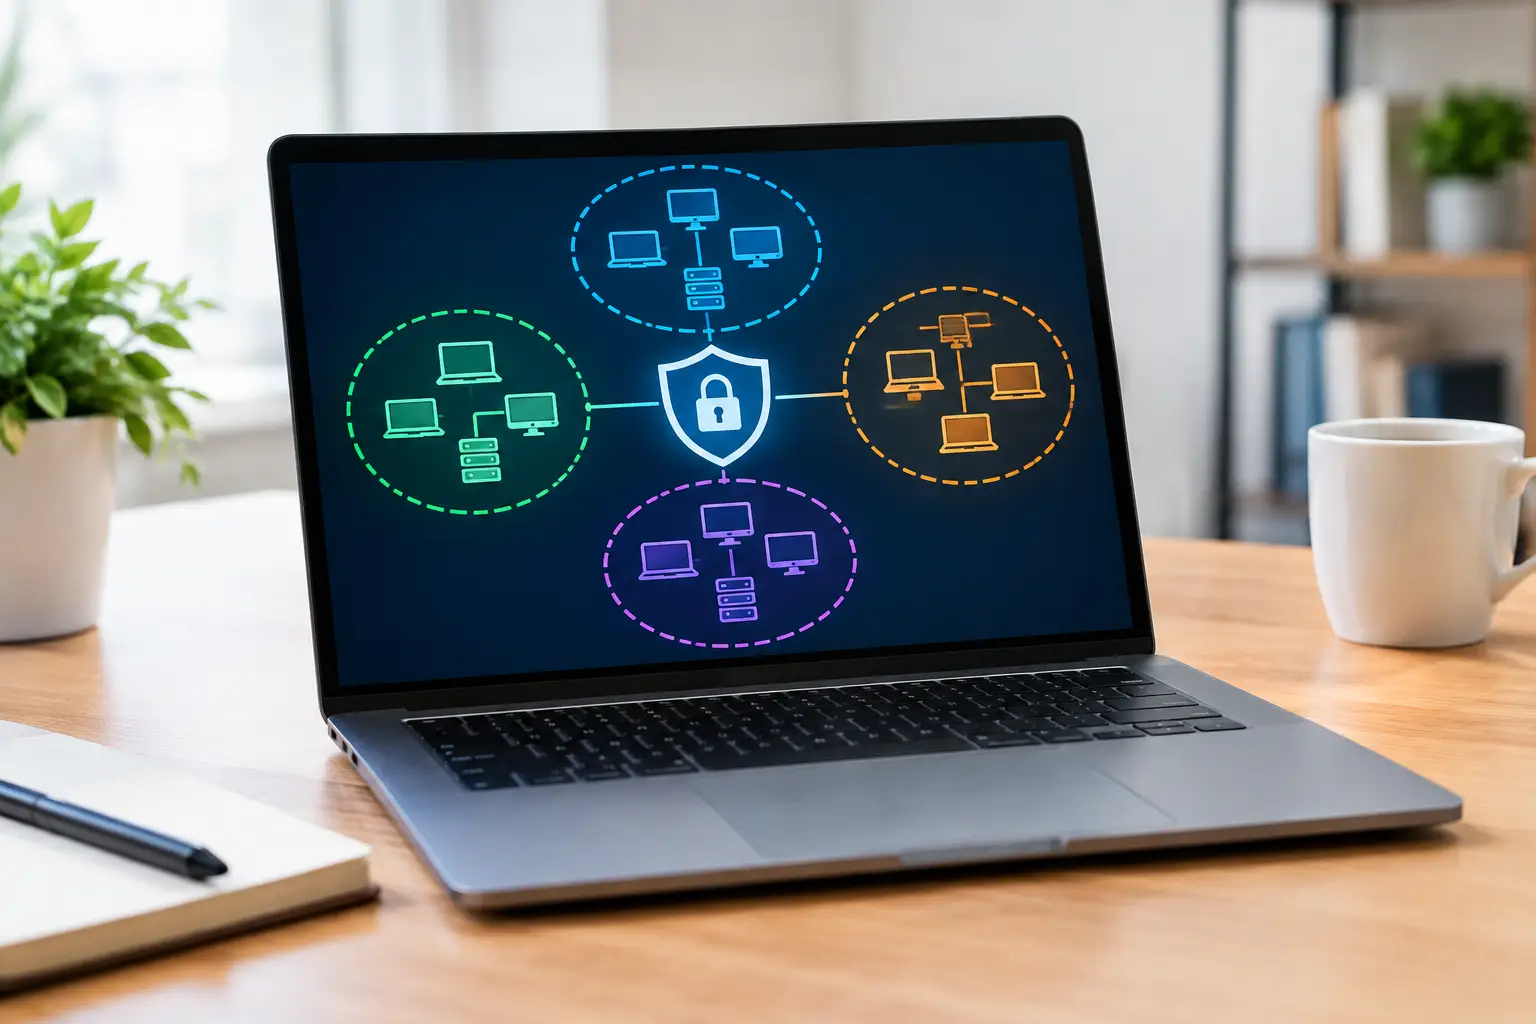
A single compromised employee laptop should not give an attacker a direct path to your accounting system, cloud backups, phone system, or patient records. That is the practical reason for network segmentation. This network segmentation guide explains how small and midsized businesses can separate critical systems, limit the spread of threats, and make their networks easier to manage.
For many organizations, the network grew one device at a time: a new wireless access point, a printer for the front office, security cameras, a guest Wi-Fi password shared with a vendor, and remote access added during a busy week. The result may work day to day, but it creates unnecessary exposure. Segmentation replaces that flat, all-access environment with clear boundaries based on business purpose and risk.
What Network Segmentation Actually Does
Network segmentation divides one network into smaller, controlled sections. Each segment has rules that define which people, devices, and applications can communicate with it. These sections are commonly created using virtual LANs, firewall policies, separate wireless networks, and access controls.
The objective is not to make every device invisible from every other device. That can create operational problems and make support harder. The objective is to allow necessary communication while blocking everything else by default.
Consider a medical practice with workstations, an electronic health record system, a guest wireless network, payment terminals, and internet-connected cameras. Those systems do not all need to communicate. A receptionist’s workstation may need access to the practice management platform and a network printer. A guest’s phone should need access only to the internet. A camera should be able to reach its approved management service, not the financial records stored elsewhere on the network.
When those boundaries are in place, one compromised device is less likely to become a company-wide incident. Segmentation also reduces accidental access, supports compliance efforts, and gives IT teams a clearer view of what is connected and why.
Why Small Businesses Need Network Segmentation
Cybercriminals often gain an initial foothold through phishing, stolen credentials, an unpatched device, or a poorly secured remote connection. Their next step is frequently lateral movement: looking for other systems they can access from the device they have already compromised.
A flat network makes that movement easier. If every device can see every other device, an attacker may be able to scan for servers, shared folders, backup appliances, printers, and administrative tools. Ransomware can then spread far beyond the original endpoint.
Segmentation limits that blast radius. If malware lands on a device in the guest network or a vulnerable internet-connected device, firewall rules can prevent it from reaching sensitive internal resources. It will not eliminate the need for endpoint protection, backups, multifactor authentication, patching, and employee awareness training. It gives those controls an additional layer of protection when one of them fails.
There is also an operational benefit. A properly organized network makes troubleshooting faster. Your IT provider can identify whether a connectivity issue is affecting a guest network, voice service, cameras, staff workstations, or a specific application rather than treating the entire office as one undifferentiated environment.
Start With Business Functions, Not Hardware
The best segmentation projects begin with an inventory, not a new firewall purchase. Before creating VLANs or changing switch configurations, identify every device, service, and data flow that matters to the business.
Document workstations, servers, cloud applications, printers, wireless access points, phones, cameras, door access systems, payment terminals, backup systems, and any equipment managed by a vendor. Ask who uses each item, what data it handles, and which other systems it must reach to function correctly.
This process often uncovers forgotten risks. An old copier may still use default credentials. A vendor may have permanent remote access that no one has reviewed in years. A line-of-business application may depend on a server that has never been included in a disaster recovery plan.
Classification should follow risk and function. A small firm might separate staff devices, servers, voice systems, guest wireless, building systems, and managed devices. A larger or more regulated organization may also need distinct segments for finance, clinical systems, development environments, payment card systems, or third-party access.
Avoid creating segments just because the hardware allows it. Every segment adds rules to maintain and potential points of failure. The right design is the simplest one that meaningfully reduces risk and supports how your employees work.
A Practical Network Segmentation Guide: Core Zones
Most small and midsized businesses can gain substantial protection from a small set of clearly defined zones. The exact design depends on your environment, but these categories provide a useful starting point:
- Business user devices: Company-managed computers and mobile devices used by employees for normal work.
- Servers and critical applications: File servers, line-of-business applications, identity services, and other systems that require stricter access controls.
- Voice and communications: VoIP phones and related equipment, separated to protect call quality and reduce exposure.
- Guest wireless: Internet-only access for visitors, contractors, and personal devices.
- Internet-connected and operational devices: Cameras, printers, smart displays, HVAC controls, door systems, and similar equipment that may have weaker security controls.
- Administrative access: Privileged IT management tools and accounts, restricted to authorized administrators and monitored closely.
A separate backup zone may be appropriate when backups are stored locally. Backups should not be freely accessible from every workstation. If ransomware compromises a user device and can reach backup storage with high-level permissions, recovery becomes much harder.
Build Rules Around Legitimate Traffic
Once zones are defined, create rules for what must communicate. This is where segmentation succeeds or fails.
Start with a deny-by-default approach between segments, then allow only specific traffic required for business operations. For example, employee workstations may need to reach a file server over approved services. The guest network should be denied access to all internal subnets. Printers may accept print jobs from staff devices but should not initiate broad connections to servers.
Rules should be specific enough to limit exposure without disrupting the business. Allowing an entire network to access a server because one application needs a single service is easy, but it defeats much of the purpose. Whenever possible, define the source zone, destination, service, and reason for each rule.
Testing matters. A rule that looks correct on paper can interrupt payroll processing, prevent a scanner from sending documents, or affect phone registration. Make changes during a planned maintenance window, communicate with affected users, and keep a documented rollback plan.
Protect Remote Access and Third-Party Connections
Remote work and vendor support can quietly bypass otherwise sound network boundaries. An employee connecting from home, a software vendor supporting a specialized application, or a security company managing cameras may all require access. The question is not whether access should exist, but whether it is limited, authenticated, and reviewed.
Require multifactor authentication for remote access. Give third parties access only to the systems they support, not the full internal network. Whenever possible, use time-limited access that is enabled for a scheduled support session and disabled afterward.
Administrative accounts deserve special attention. A user account that can manage network equipment, servers, and cloud platforms should not also be used for routine email and web browsing. Separating administrative access reduces the chance that a phishing event becomes a complete infrastructure compromise.
Monitor, Review, and Maintain the Design
Segmentation is not a one-time project. New employees, office expansions, cloud migrations, and vendor changes all affect the network. Firewall rules that were reasonable two years ago may now be too broad, unnecessary, or undocumented.
Review segmentation rules regularly and remove access that no longer serves a business purpose. Monitor for blocked connection attempts, unusual traffic between zones, and unmanaged devices appearing on the network. Those signals can reveal a misconfiguration, a shadow IT problem, or suspicious activity that deserves investigation.
Keep network diagrams and rule documentation current. During an outage or security incident, the ability to understand the environment quickly has real business value. It reduces guesswork, shortens recovery time, and helps decision-makers communicate clearly with staff, customers, and vendors.
For organizations without an internal network security team, a managed IT partner can assess the existing environment, identify high-risk gaps, and implement a design that fits the budget and operational needs. ZeroIn approaches segmentation as part of a broader strategy for uptime, cybersecurity, and business continuity, not as a standalone hardware project.
The next useful step is to look at your own network through a simple question: if one device were compromised this afternoon, what else could it reach? The answer will show where better boundaries can protect your business before a routine problem becomes a costly interruption.